
 $
 EGP
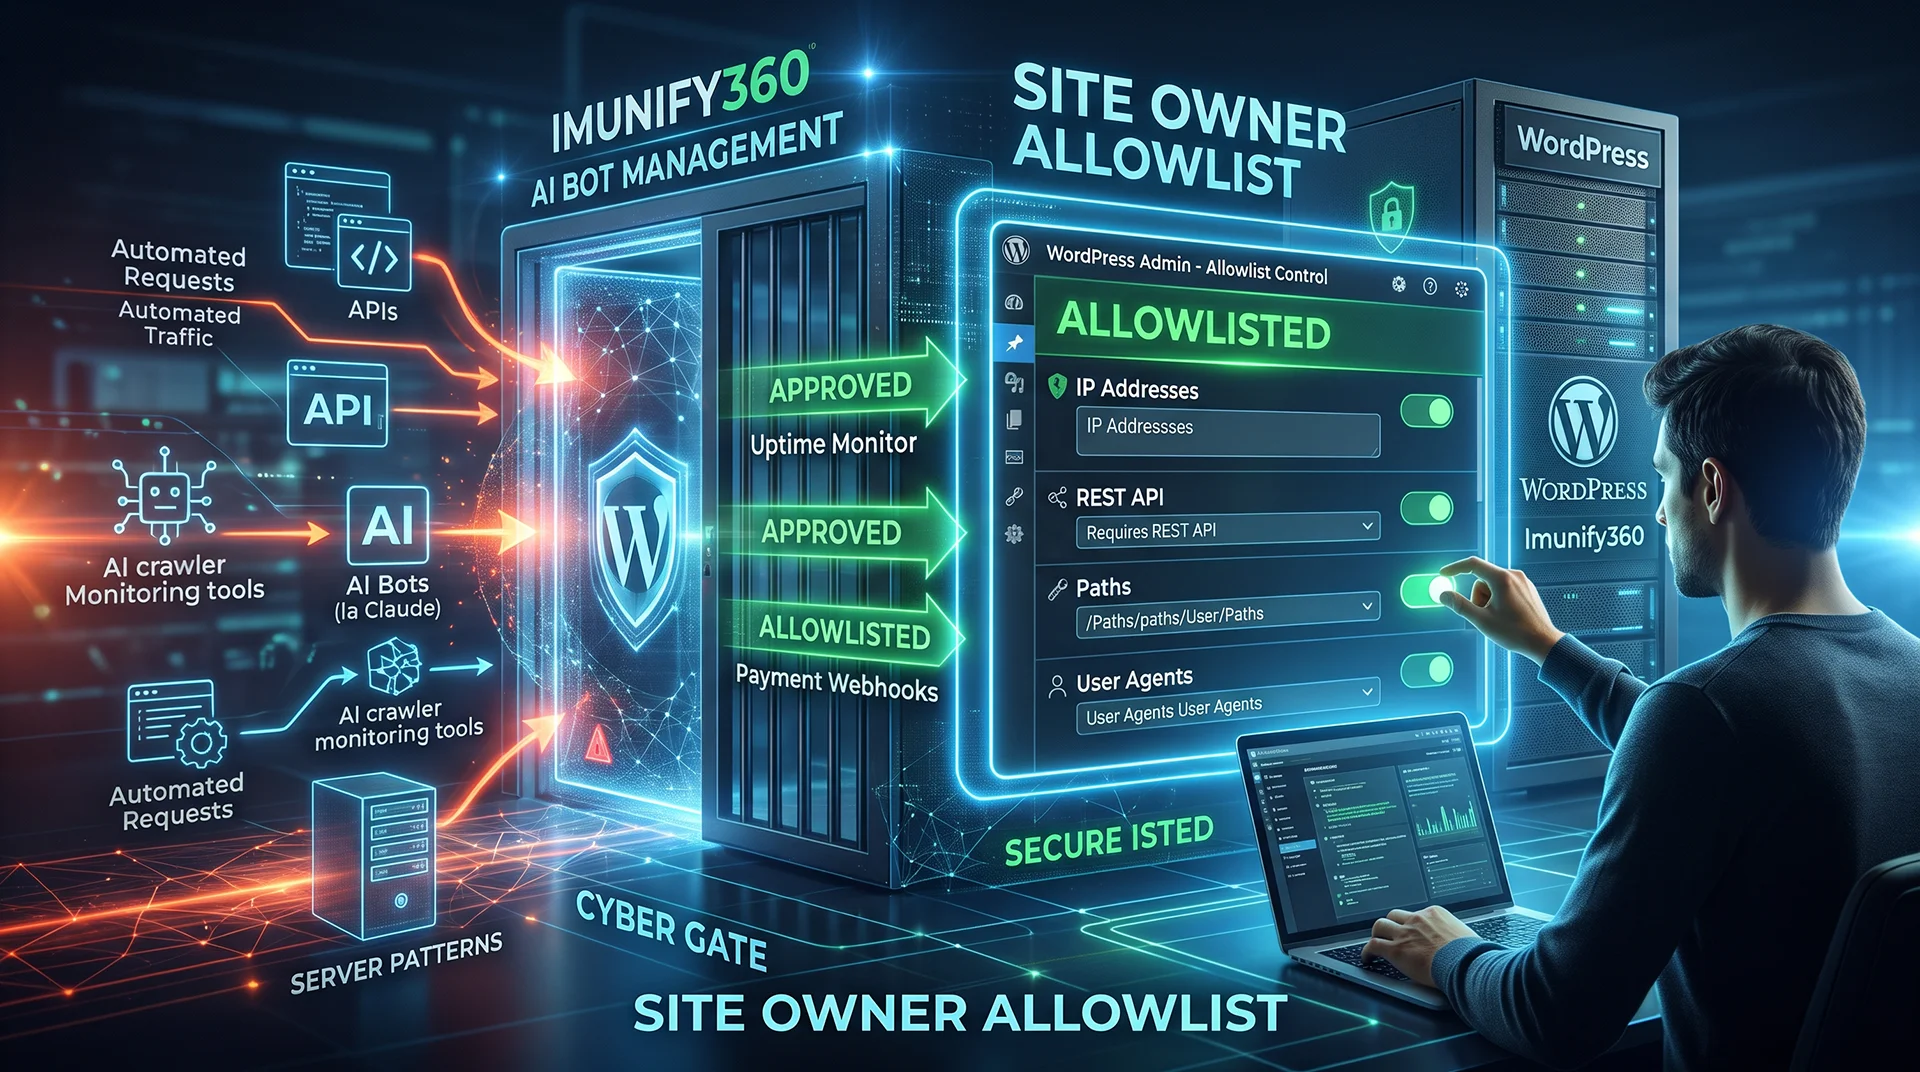
With Imunify Security for WordPress 4.1.4+, site owners can add their own allowlist for AI Bot Management from WordPress admin. Matching requests are no longer classified, rate-limited, or blocked on that site—so legitimate tools like uptime monitors and payment webhooks keep working without waiting on a support ticket for every exception.
On Brmgina hosting, this is for you as the WordPress site owner when the Bot Traffic / allowlist tools are available on your site. It does not replace updating plugins or good security habits.
What problem does this solve?
AI Bot Management sorts automated traffic and rate-limits AI crawlers and other bots so heavy crawling does not slow the site.
Some “bot-looking” traffic is actually required:
- An uptime monitor hitting the same page every minute
- A payment provider calling a webhook in bursts at checkout
- Other integrations that identify as automated clients
Previously, exempting that traffic often meant asking the host to change a server-wide whitelist. Now you can add site-level exceptions yourself in WordPress when the feature is available.
What you can allowlist
Each entry is one of four types (you can add an optional note explaining why it exists):
- IP address or CIDR range — for example a monitoring service’s fixed IPs
- Page path — a specific URL path on your site
- REST API route prefix — useful for headless fronts or integrations
- User agent — the client name the request sends
Every request is checked against the allowlist first. A match bypasses classification and rate limits and is counted as Allowlisted in the Bot Traffic dashboard.
Important notes for WordPress users
- Entries apply to this site (site-level). They are separate from any server-wide hosting rules.
- Provider / Imunify rules may still appear on the page as read-only. You cannot remove those.
- User-agent allowlists are weaker: any client can claim any name. If a service publishes fixed IPs, allowlist the IPs instead.
- On WordPress Multisite, allowlist entries apply network-wide and only a super admin can edit them.
How to use it
- Open WordPress Admin and go to the Imunify Security Bot Traffic page.
- Add an allowlist entry (IP, path, REST route prefix, or user agent) and save a short note for yourself.
- Use the Bot Traffic dashboard to see allowlisted requests counted separately from humans and bots.
- Use Check a request to test whether a sample request matches a rule—and which one.
If you do not see Bot Traffic / allowlist options, the feature may not be available on that site yet. Contact Brmgina support and we can check your hosting account.
Useful extras in this release
- Claude traffic (Claude-User) is recognized as verified AI traffic and checked against Anthropic’s published IP ranges—so it is not treated as an unverified bot the same way as before.
- On Elementor sites, Elementor’s MCP endpoint used by AI assistants is no longer rate-limited for that route (that exemption is for that endpoint only).
Quick checklist
| Goal | What to do |
|---|---|
| Uptime monitor keeps getting limited | Allowlist the monitor’s IP range if published; avoid user-agent-only if possible |
| Payment / webhook bursts fail | Allowlist the webhook path or the provider’s IPs / REST route |
| Confirm an entry works | Use “Check a request” on the Bot Traffic page |
| No Bot Traffic allowlist in admin | Contact Brmgina support |
Conclusion
The site-owner allowlist in Imunify Security for WordPress gives you direct control over exceptions for AI Bot Management—ideal for monitors, webhooks, and trusted integrations—while still letting Imunify protect the site from unwanted bot load.
Source / further reading: Imunify360: site owners can now allowlist traffic.
